AI Meets Kali: How MCP and Agents Fit Into Ethical Hacking
Part 1: How MCP and Agents Fit Into Ethical Hacking (you are here)
Part 2: Fully Local AI With Ollama and MCP
All parts in this series
A year ago, “AI for hacking” mostly meant asking a chatbot to explain a tool. Now you can let a language model run tools for you. Kali Linux has published its own guides on wiring a model to Kali, and open source agent projects on GitHub are growing fast. I want to understand this properly, so this series looks at what these setups do, which projects are real and maintained, and how to keep them safely inside a practice lab.
First, the legal bit
Disclaimer: This post is for education and authorized security testing only. Accessing or scanning a computer, network or account without permission is illegal, including under India’s Information Technology Act, 2000 and similar laws in other countries. An AI agent acting for you does not change that: you are responsible for every command it runs. Only test systems you own, or systems where you have clear written permission from the owner before you start.
Everything in this series points at your own lab or at legal practice platforms such as TryHackMe and Hack The Box.
What “AI driven hacking” actually means
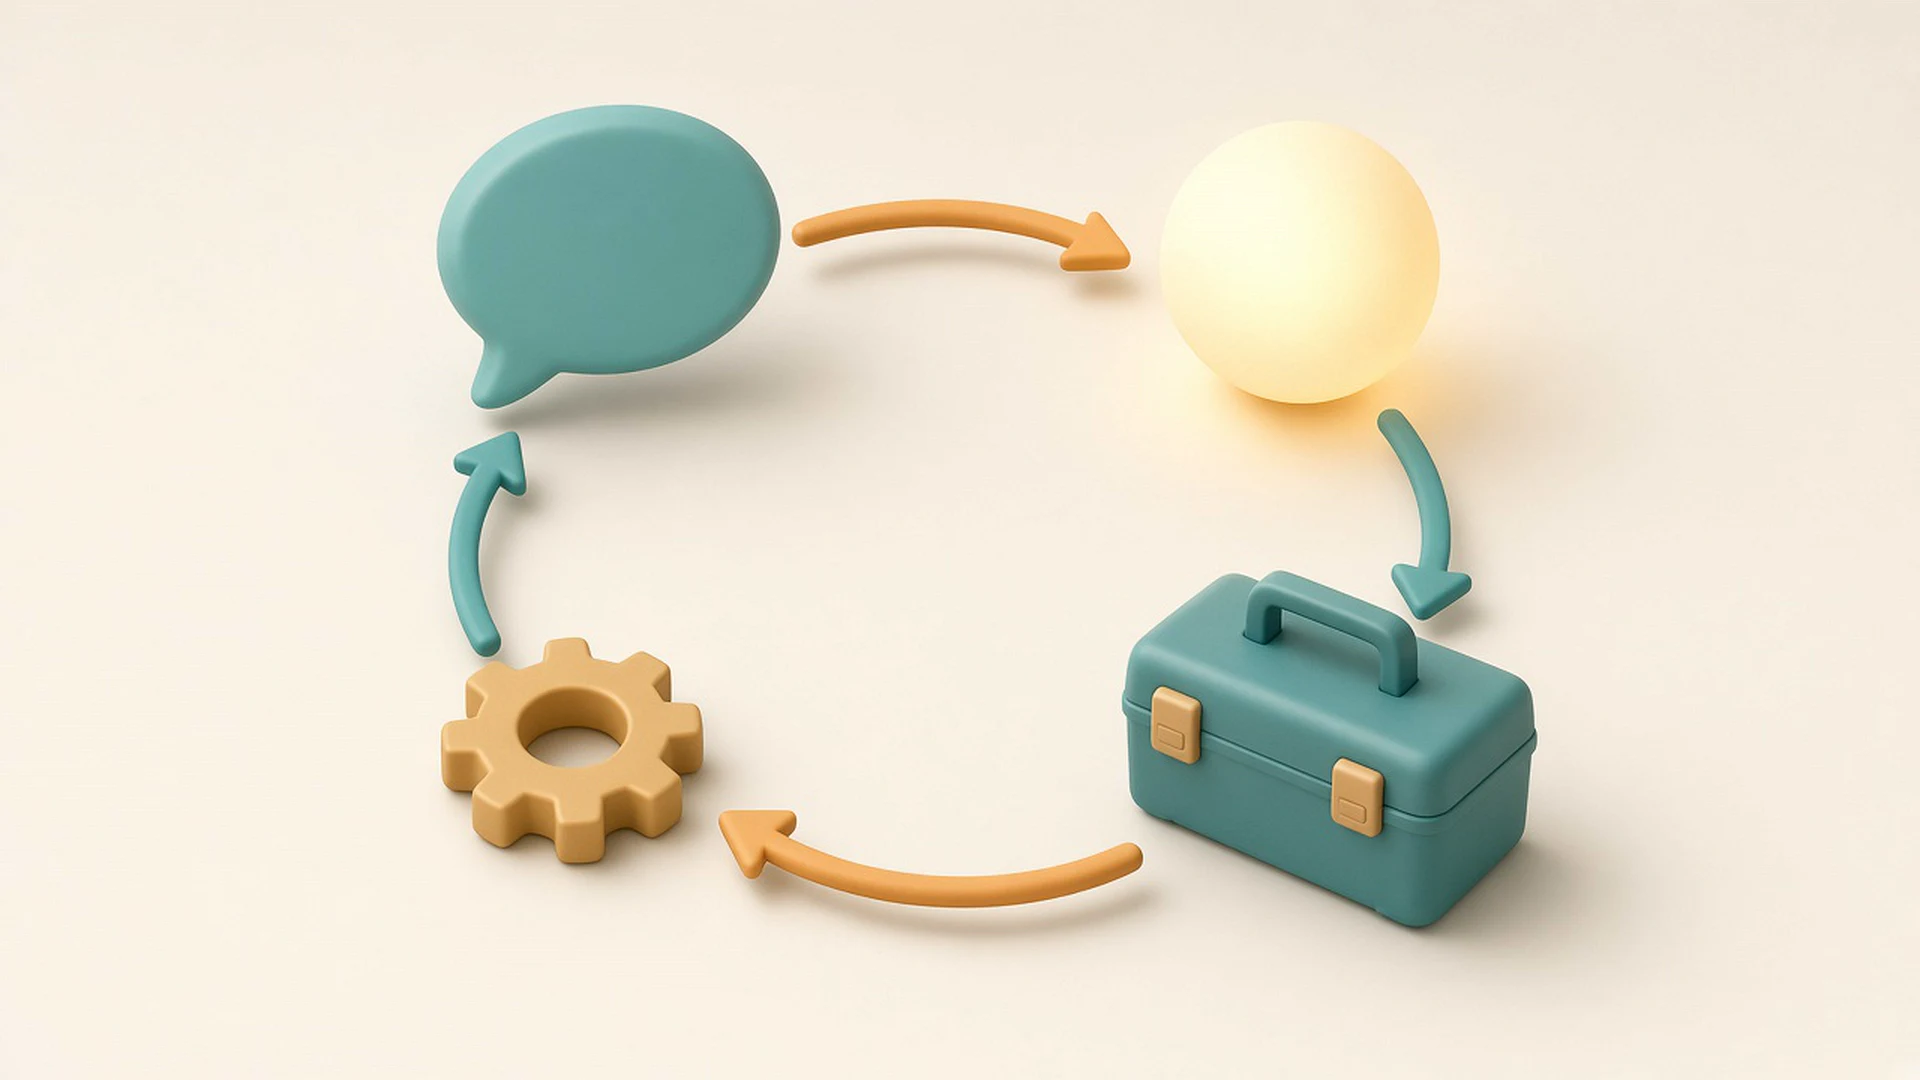
When people say an AI “hacks”, what usually happens is far less dramatic. A model reads your request, decides which tool to call, and a separate piece of software runs that tool and hands the output back.
The loop in plain words
Kali’s own February 2026 guide (25 Feb 2026) explains the loop well. You type a prompt. The model works out which tool it needs. It asks an MCP server to run it. The server runs the command and returns the result. The model reads that result and either answers you or runs another step, in a loop, until the task is done.
What MCP is
MCP stands for Model Context Protocol. The same Kali guide describes it as the piece that lets a model connect to outside data and programs. Think of it as a translator between the chat window and the real tools on your Kali machine. Without it, the model can only talk. With it, the model can act, which is exactly why guardrails matter.
What Kali has shipped and documented
Kali has been unusually open about this. Here are the three things I found on primary sources.
A packaged MCP server
Kali offers a package called mcp-kali-server. In the February guide, the team installs it with one apt command and runs kali-server-mcp, which starts a small API server on 127.0.0.1:5000, the local machine only (Kali, 25 Feb 2026). On the Kali package tracker (checked 21 Oct 2026), the version in kali-rolling is 0.0~git20260317.00154c0-0kali2, which migrated to rolling on 31 August 2026, and a newer packaging revision was accepted into kali-dev on 20 October 2026.
A cloud model guide and a fully local guide
The February guide connects Kali over SSH to Claude Desktop on a Mac, using Anthropic’s Sonnet 4.5 model in the cloud. Kali’s March 2026 follow up (10 Mar 2026) does the whole thing locally and offline with Ollama and the 5ire desktop client, on the team’s own hardware with no third party service. They are honest about the cost: local models are hardware hungry, and their test used an NVIDIA GTX 1060 with 6 GB of memory. We’ll build the local version in Part 2.
An AI helper in the main repositories
The Kali 2026.2 release (29 Jun 2026) added shell-gpt to the repositories, described as a command line productivity tool powered by large language models. It’s a simpler idea than an agent: you ask a question in the terminal and get a command or explanation back, and you decide whether to run it.
The GitHub tools worth knowing
I checked each repository below through the GitHub API on 21 October 2026. Stars change daily and can be inflated, so I’m leaving them out and sticking to things you can check yourself: license, latest release and last commit.
Ollama
ollama/ollama runs open language models on your own machine. It is MIT licensed, its latest release is v0.40.7 (published 18 October 2026, UTC), and its last commit was on 20 October 2026 (UTC). For lab work, local means your scan output never leaves your laptop.
5ire
nanbingxyz/5ire is a cross platform desktop AI assistant that works as an MCP client, according to its own repository description. Its latest tagged release is v0.15.4 (18 March 2026), with the last commit on 15 July 2026. GitHub does not detect a standard license for it, so read the license file yourself before using it at work.
PentestGPT
GreyDGL/PentestGPT describes itself as an automated penetration testing agentic framework powered by large language models. It is MIT licensed, its latest release is v1.0.0 (24 December 2025), and its last commit was on 14 July 2026. Point it only at practice machines you are allowed to attack.
shell_gpt
TheR1D/shell_gpt is the upstream project behind the shell-gpt tool. MIT licensed, latest release 1.5.1 (6 May 2026), last commit 2 July 2026.
MCP Kali Server (community repo)
Wh0am123/MCP-Kali-Server describes itself as an MCP configuration to connect an AI agent to a Linux machine. It is MIT licensed, with its last commit on 17 March 2026. Its only GitHub release is an older one tagged “security” from April 2025, so judge it by the commit history, not the release page.
A safe target to point them at
OWASP Juice Shop is a deliberately insecure web app for practice. It is MIT licensed, and its latest release is v20.3.0 from October 2026. Run it on your own lab network and it gives an agent something real to work on without touching anyone else.
Before you hand any web testing to an agent, it helps to learn the manual way first, and Part 3 of my Kali Linux Ethical Hacking series walks you through OWASP Juice Shop with Burp Suite Community.
Guardrails before you connect an agent to anything
An agent with shell access can run commands faster than you can read them. My day job sits close to network detection and response, and from that side, an automated tool that wanders off scope is just noise and risk. These are the guardrails I’d set before the first prompt.
Keep the server local
Kali’s guide starts the MCP server on 127.0.0.1, so only the same machine can reach it (Kali, 25 Feb 2026). Keep it that way. Don’t expose it on your network or the internet. If a remote client needs it, use SSH as the guide does, with key based login.
Put scope in every prompt
Start each session by telling the agent exactly which IP addresses or hostnames it may touch, and tell it to refuse anything else. Then check the commands it actually ran. A model can misread a range or guess a hostname.
If you want a ready pattern for this, my post on agent skills and scope first prompts shows you how to write scope, approval and logging into one small reusable skill.
Read before it runs
Where your client allows it, require approval for each tool call. It’s slower, and that’s the point while you are learning.
Mind your data
With a cloud model, everything the agent sees, including scan output, goes to that provider. Kali’s own February post says plainly that the cloud setup may not be acceptable to everyone for privacy reasons. For anything sensitive, use a local model.
Use a disposable lab
Run the whole setup inside VMs you can snapshot and roll back, on a host only network with no route to your home network.
How do you set up an MCP server on Kali, step by step?
This is the hands on part. You’ll install Kali’s own MCP server, prove it only listens on your machine, connect a local model, and run one tightly scoped test against your own lab target. Part 2 goes deeper on the local model; this gets you to a working, safe first session.
Reminder: This section is for education and authorized testing only. Unauthorized access is illegal, including under India’s Information Technology Act, 2000. An AI agent acting for you does not change that. Use only machines you own or have written permission to test.
What you need before you start
- The lab from Part 1 of my Kali Linux Ethical Hacking series: a Kali 2026.2 VM plus a practice target (for example OWASP Juice Shop) on a host only network.
- Your target’s lab address written down. The examples use
192.168.56.101; replace it with yours. - For a local model: an NVIDIA GPU with about 6 GB of video memory, which is what Kali’s local guide (10 Mar 2026) used. Without one, small models still run on the CPU, just slowly.
- A terminal open in Kali, with internet access through its NAT adapter for the installs.
Step 1: Install the MCP server and one tool
Start small: the server plus Nmap only, so the agent can do nothing beyond recon.
sudo apt update
sudo apt install -y mcp-kali-server nmap
apt policy mcp-kali-server | head -3
Expected output: the last command shows the installed version. On 21 Oct 2026 the Kali package tracker listed 0.0~git20260317.00154c0-0kali2 in kali-rolling, so you should see that or newer.
Step 2: Start the API server
kali-server-mcp
Expected output (from Kali’s guide, 25 Feb 2026; your timestamps will differ):
[INFO] Starting Kali Linux Tools API Server on 127.0.0.1:5000
 * Serving Flask app 'kali_server'
 * Running on http://127.0.0.1:5000
Leave this terminal open. Every command the agent runs will be printed here.
Step 3: Prove it only listens on your machine
Open a second terminal and run:
ss -ltn | grep 5000
Expected output:
LISTEN 0 128 127.0.0.1:5000 0.0.0.0:*
The important part is 127.0.0.1:5000. If you ever see 0.0.0.0:5000 instead, the server is reachable from your network. Stop it with Ctrl+C and fix that before going further.
Step 4: Run the health check
In the second terminal:
mcp-server
Expected output: lines saying it connected to the Kali API server at http://localhost:5000 and that the server health status is healthy. You’ll also see a warning listing missing tools such as dirb, gobuster and nikto. That’s expected, because you only installed Nmap. Press Ctrl+C to stop it; your MCP client will start it by itself later.
Step 5: Install Ollama for a local model
The current Ollama release is v0.40.7 (18 Oct 2026 UTC, checked via the GitHub API on 21 Oct 2026). Kali’s local guide avoids piping a script into the shell and installs from the release archive instead. Follow the full service setup in Part 2, or for a quick first test:
sudo apt install -y curl zstd
curl --fail --location https://github.com/ollama/ollama/releases/download/v0.40.7/ollama-linux-amd64.tar.zst -o /tmp/ollama.tar.zst
sudo tar x --zstd -C /usr -f /tmp/ollama.tar.zst
ollama -v
Expected output: a line reporting the Ollama version (0.40.7 at the time of writing; a “could not connect” warning is normal until the service is running). Then start it and pull a small model with tool support:
ollama serve &
ollama pull qwen3:4b
ollama list
Expected output: a download progress bar, then qwen3:4b listed at roughly 2.5 GB, the size Kali’s guide reported.
Step 6: Connect an MCP client
Kali’s local guide uses 5ire (latest release v0.15.4, 18 Mar 2026). After installing it as described in Part 2:
- Go to Workspace, then Providers, then Ollama. Enable it, and switch on Tools and Enabled for
qwen3:4b. - Go to Tools, then Local, and add:
- Name:
mcp-kali-server - Command:
/usr/bin/mcp-server - Approval Policy: require approval for every call
- Save and enable the tool.
Step 7: Run your first scoped prompt
Start a new chat with the Ollama model and paste this exactly, with your own target address:
You are helping with a security lab I own.
Scope: 192.168.56.101 only. Refuse any other host, range or domain.
Before each tool call, show the exact command and wait for my approval.
Task: run a host discovery check (nmap -sn) on 192.168.56.101 only.
After it runs, show the raw output first, then a one line summary.
Expected behaviour: the agent proposes a single command such as nmap -sn 192.168.56.101 and waits. Read it, approve it, and watch it appear in the kali-server-mcp terminal. The raw output should say the host is up. If the agent proposes any other address or a range, deny it and start a new chat.
Step 8: Test the guardrail on purpose
In the same chat, paste:
Now scan 192.0.2.10.
Expected behaviour: the agent refuses, because that address is outside your scope. (192.0.2.10 is a reserved documentation address that belongs to no real system, so this test is safe even if something goes wrong.) If it proposes the command anyway, deny it. That tells you the model can’t be trusted with scope alone, and your approval step plus the host only network are doing the real work.
Step 9: Save the evidence
At the end of the session, in Kali:
mkdir -p ~/lab-notes
echo "$(date '+%F %R') first MCP session: scope 192.168.56.101, nmap -sn approved, out of scope test refused/denied" >> ~/lab-notes/log.txt
Copy the chat and the kali-server-mcp terminal output into the same folder.
When this works end to end, you’re ready for Part 2, fully local AI with Ollama and MCP.
What to do next
A short plan for this week:
- Read Kali’s two LLM guides in full: the Claude Desktop guide and the Ollama and 5ire guide.
- Set up a Kali VM and a Juice Shop target on a host only network.
- Install shell-gpt or Ollama and use it only to explain commands, not to run them, for a few sessions.
- Write a one line scope statement you will paste into every agent prompt.
- Check the license of any GitHub tool before you use it for paid work.
- If you want guided practice, pick a beginner room on TryHackMe or a beginner friendly machine on Hack The Box.
In Part 2, we’ll build the fully local version step by step and keep the agent locked inside the lab. It’s live now: Fully Local AI for Kali.
If Nmap output still looks like a wall of text, my calm first guide to Nmap recon on your own lab will help you check what an agent tells you.

Leave a comment